Security leadership that goes beyond advice.
Fractional CISO and Head of Security services for technology companies, combining senior strategic leadership with hands-on technical expertise in Product Security, secure engineering, and AI Security.
A security leader who can work with your engineers.
A useful security strategy has to survive contact with the product roadmap. Ascensis brings executive-level judgment and the technical depth to help teams make better architecture, development, and risk decisions.
Work directly with founder Chris Martorella to set priorities, lead the security function, and guide implementation with the people building your product.
From security strategy to certification.
Experience leading startups through ISO 27001 and SOC 2 initiatives, turning compliance requirements into practical security controls that support enterprise growth.
Leadership, built into the work.
Choose an embedded security leader or focused technical advisory. Each engagement is shaped around the product, team, and decisions in front of you.
Fractional CISO & Security Leadership
Embedded security leadership combining strategy, governance, hands-on technical guidance, and ISO 27001, SOC 2, and enterprise readiness.
Explore this service 02 / BUILDProduct Security & Secure SDLC
Practical security architecture, threat modeling, AppSec, DevSecOps, and engineering enablement across the product lifecycle.
Explore this service 03 / EMERGING SYSTEMSAI Security & Secure AI Product Development
Secure design and integration for LLM applications, RAG, agents, and AI-assisted development, grounded in real product work.
Explore this serviceSecurity belongs in the product lifecycle.
We connect business priorities to the engineering decisions where risk is created or reduced. The work can begin with a strategic question and continue through design, delivery, and learning.
Plan
Set risk priorities, ownership, and investment decisions.
Design
Review architecture and model threats early.
Build
Enable secure development and useful automation.
Verify
Test assumptions and assess security before release.
Operate & Improve
Manage vulnerabilities and feed lessons into the next cycle.
Led security. Built security tools. Worked inside product teams.
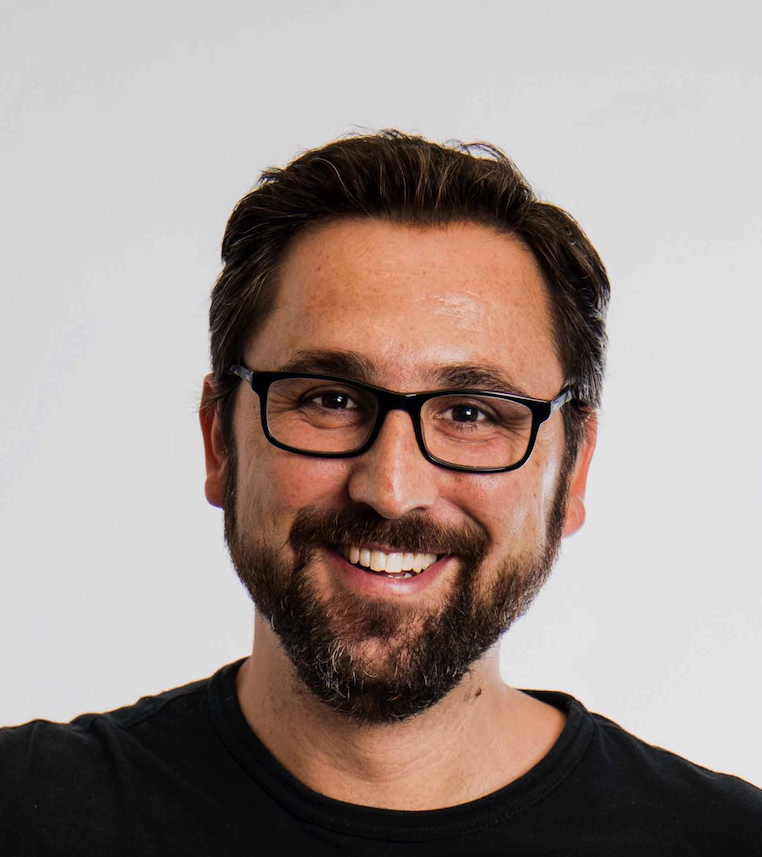
Chris Martorella was Head of Product Security at Miro and CISO at Skyscanner, with previous experience at Microsoft, Skype, and Verizon Business. His background also includes offensive security and contributions to open-source tools including theHarvester and Wfuzz.
Direct access. Clear ownership. Practical progress.
Understand the context
We learn your product, team, growth plans, and current security decisions before setting priorities.
Work alongside your team
Engage as a fractional leader or on a defined technical initiative, in the tools and rhythms your team already uses.
Leave capability behind
Document decisions, mentor people, and help build practices that keep working after the engagement.